mTLS in Practice: Certificates for Service Auth
Mutual TLS makes the client prove its identity with a certificate too. Here is the nginx config, the client commands, and the error you get when one is missing.
Read more
Feedback Loops: Catching Complaints Before Listings
When a recipient hits the spam button, a feedback loop sends the complaint as a structured ARF report. Here is what is inside one and how to trace it back.
Read more
RSA vs ECDSA: Choosing Certificate Key Algorithms
ECDSA P-256 is the right default for new certificates: smaller keys and faster signing, with RSA as a fallback for legacy clients. Numbers, commands, config.
Read more
Wildcard vs SAN Certificates: Choosing the Right One
A wildcard covers every subdomain from one key; a multi-SAN cert names each host. One hides your hostnames, the other limits the damage. Default to named certs.
Read more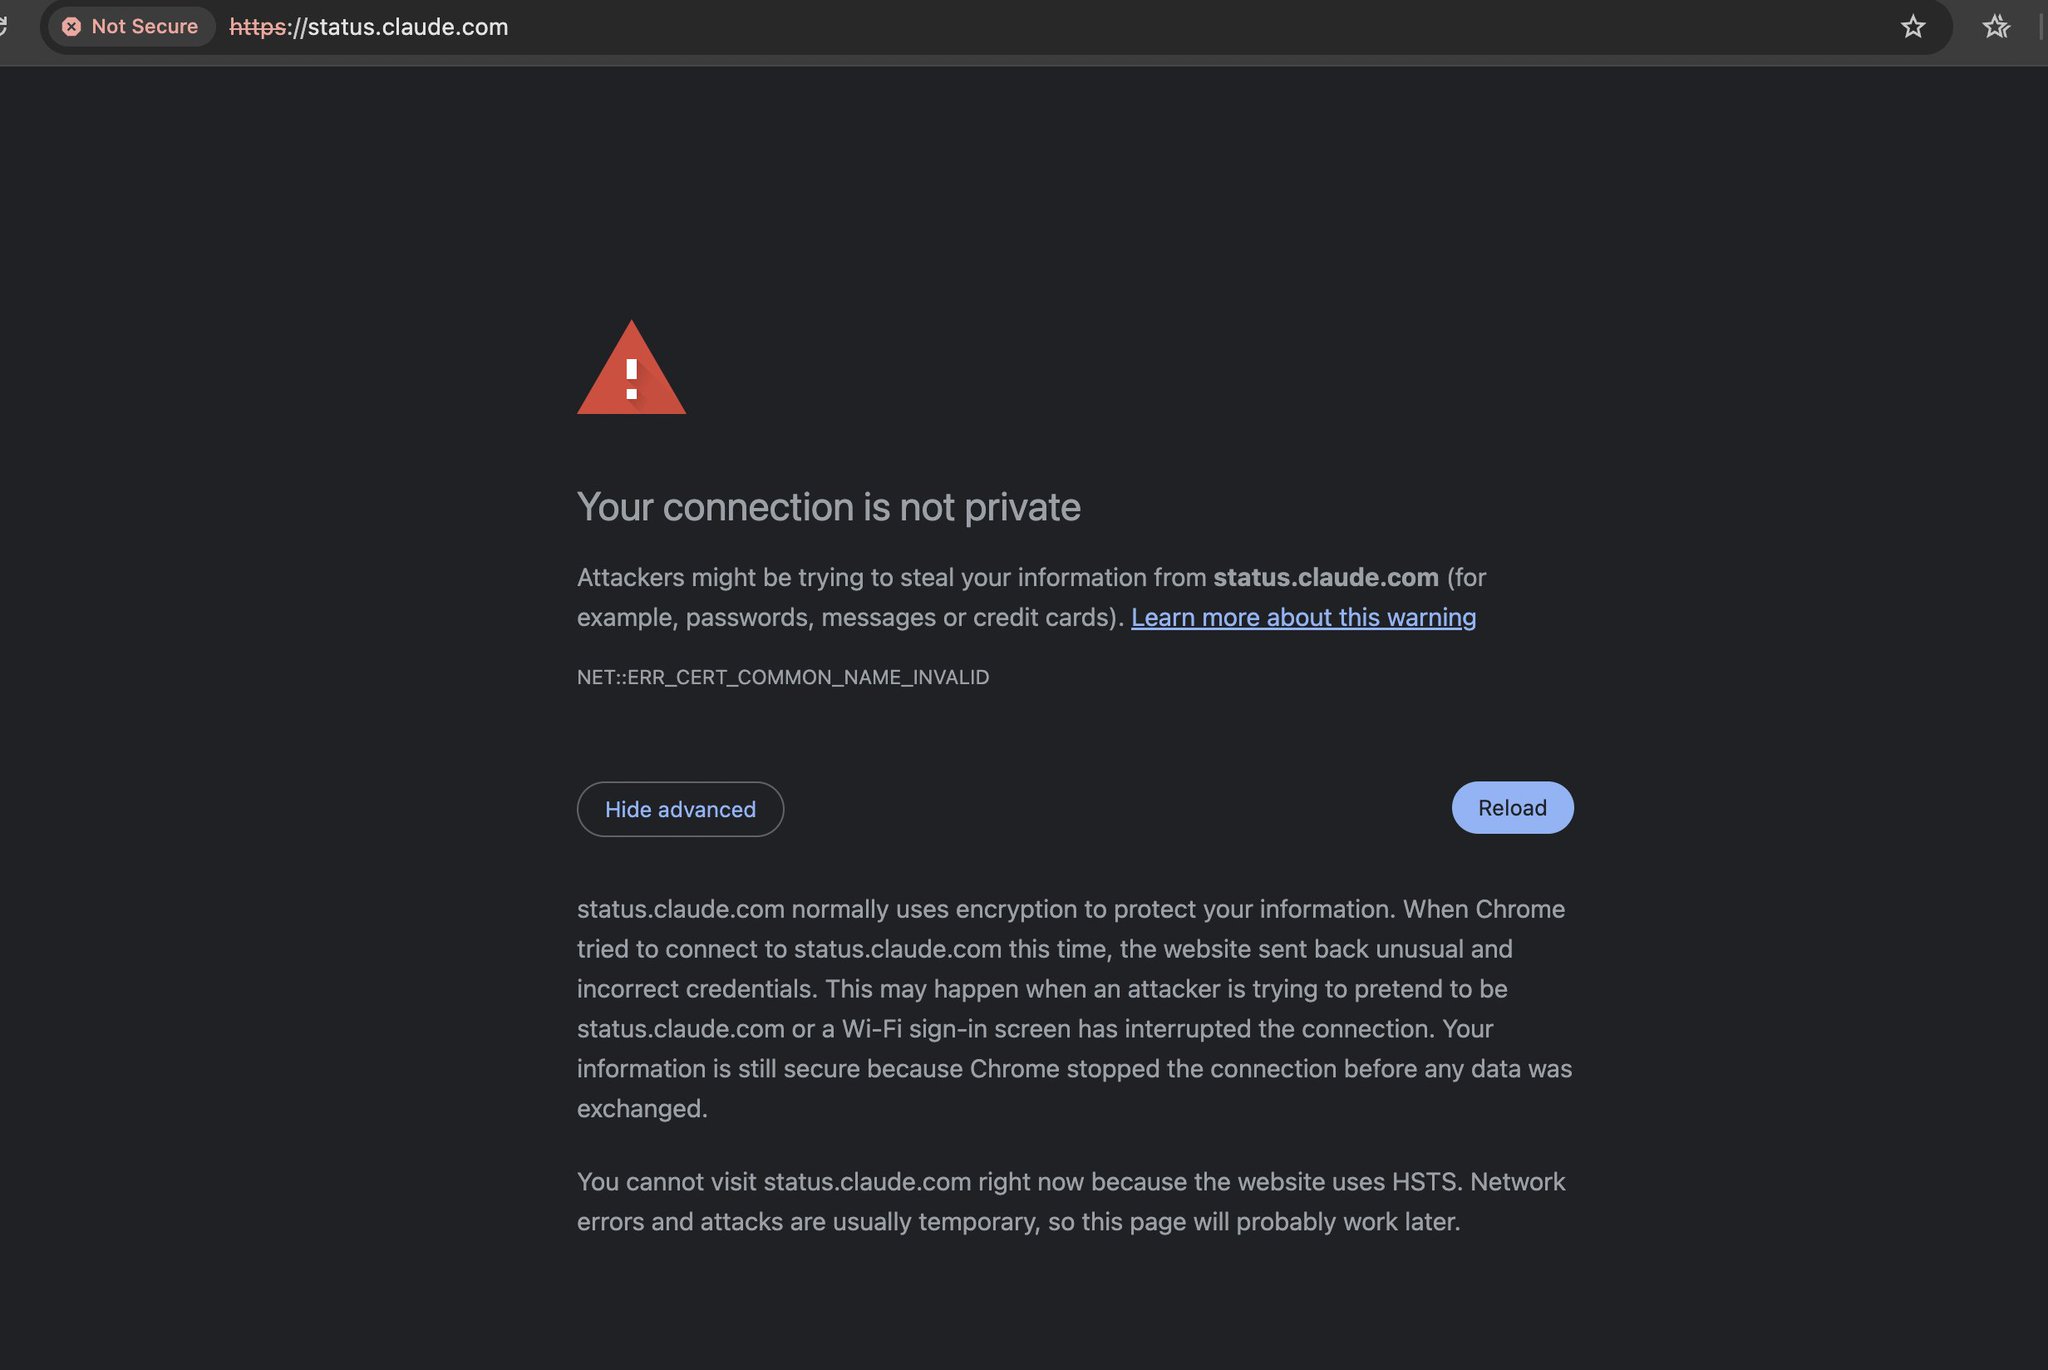
When a Certificate Takes Down the Status Page
On August 14, 2026, an invalid TLS certificate blocked Claude's own status page. If a near-trillion-dollar company can miss a certificate, so can you.
Read more
Shared vs Dedicated Sending IPs: Managing Blacklist Risk
A dedicated sending IP sounds like an upgrade, but for most senders it is a self-inflicted deliverability wound. Here is when each model is the right call.
Read more