Email & Domain
Blacklist Monitoring
Monitor IPv4, IPv6 addresses, and domains against 150+ blocklists and data sources in real-time. Instant alerts protect your email deliverability and reputation.
Monitoring mail infrastructure for thousands of companies, from startups to the Fortune 500
From Listed to Fixed,
Without the Hunting
Add Your Hosts
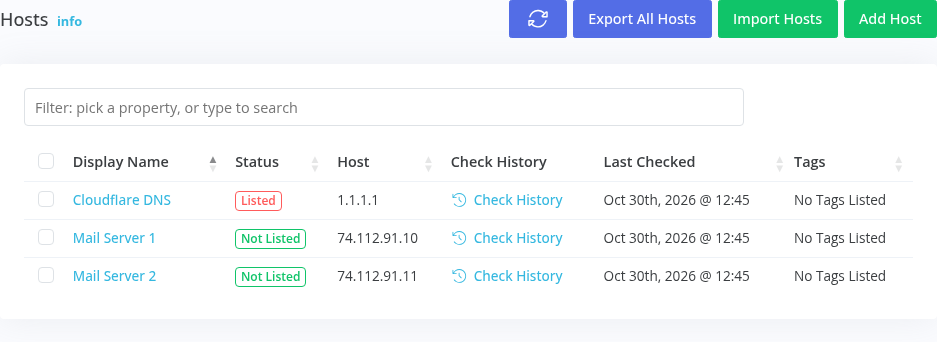
List individual IPv4 and IPv6 addresses, CIDR ranges, or domains. Bulk import a list, or manage hosts through the REST API.
We Check Around the Clock
Every host is checked on a schedule against RBLs, URIBLs, DNS filters, and threat exchanges, picked and maintained by us.
You Get the Alert, and the Why
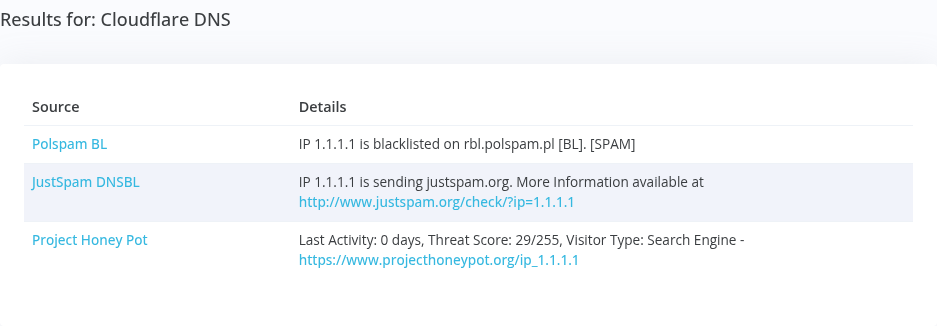
The moment a host is listed, the right people hear about it, with which data source flagged it and why, so you fix the cause instead of hunting for it.
Blacklist Monitoring in Under Two Minutes
Add hosts, choose the lists that matter, follow a listing from alert to removal, and share the results.
What You Actually Work
With Every Day
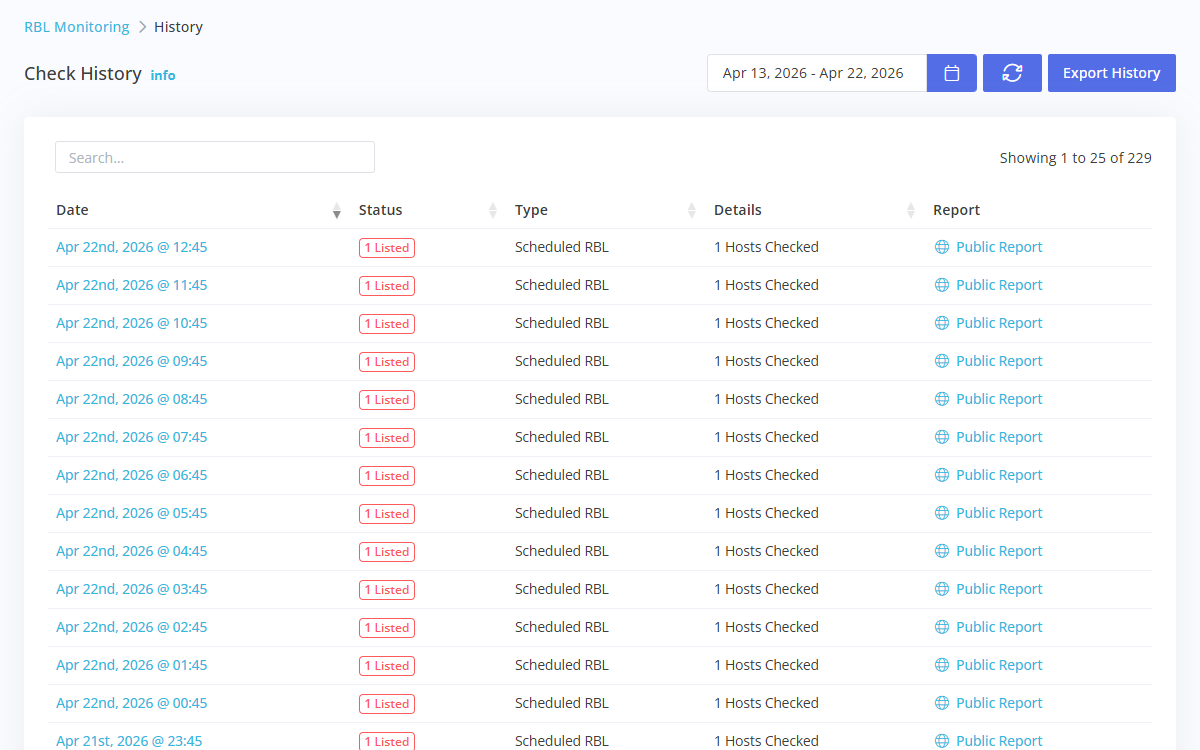
Listings Get Expensive by the Hour.
Every hour you're listed, mail bounces and sender reputation decays. We close that gap to minutes and tell you which data source flagged you and why, so you're fixing the cause, not hunting for it.
Every Listing, Explained.
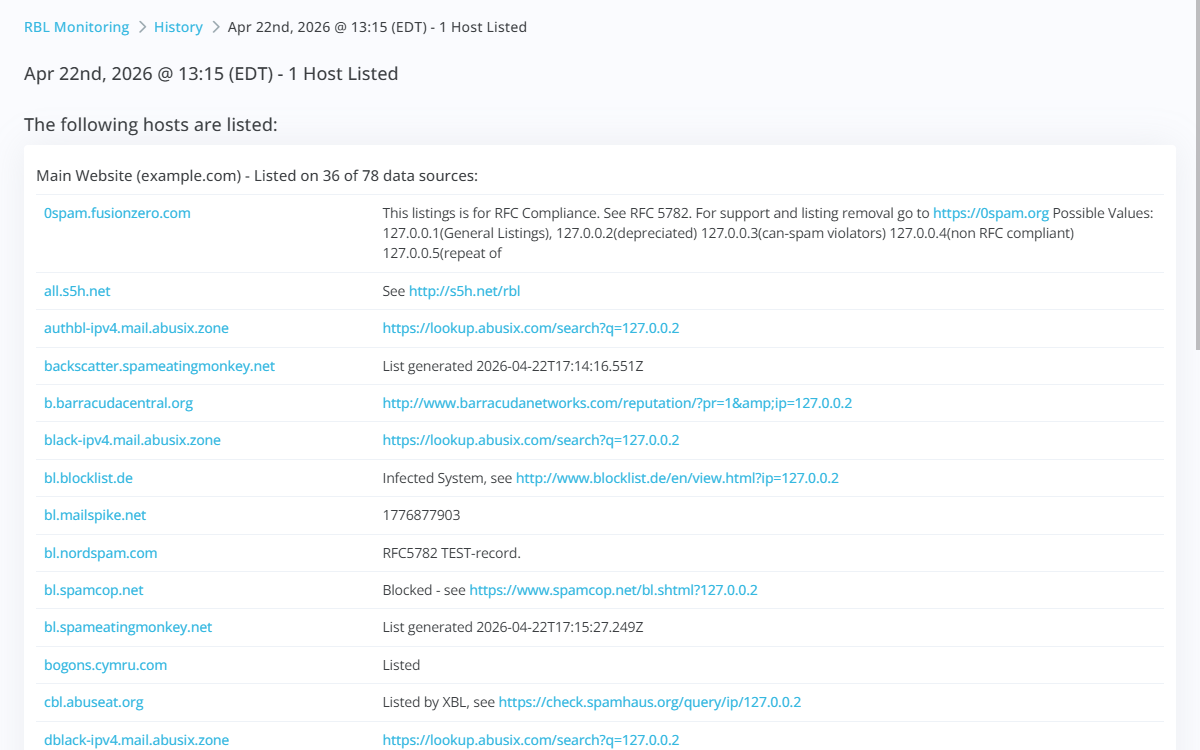
Each listing shows the data source, the reason it gave, and where to go next, so the first person to see the alert can start the fix.
Which Data Sources to Trust Is Our Problem, Not Yours.
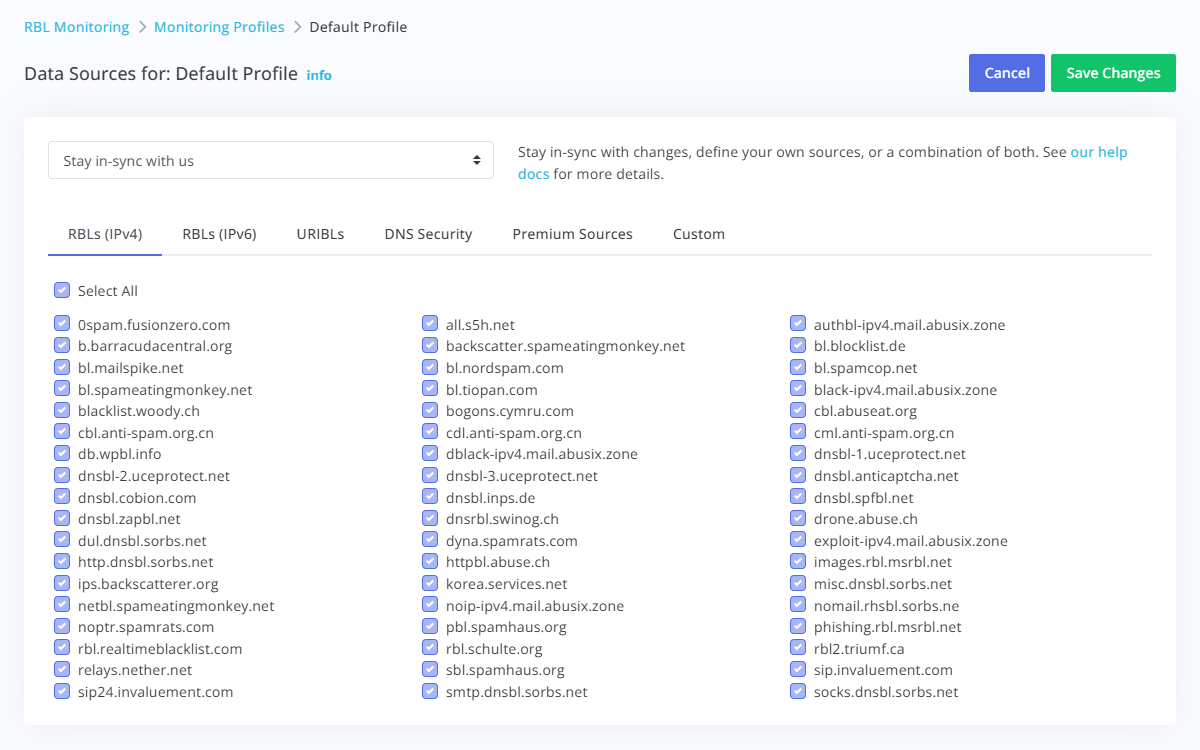
We evaluate data sources, track reliability, and swap out stale providers so the curated default stays current. Customize the selections when you know what you want; rely on the defaults when you don't.
Hand Over Proof, Not Prose.
When your mail stops flowing, an ISP or customer will ask for proof. A public report they can open and verify themselves ends the conversation on the first reply.
What Is Blacklist Monitoring?
Blacklist monitoring, also called RBL monitoring, is a service that checks your IP addresses and domains against the blacklists receivers use and alerts you the moment one lists you.
Protect Email Deliverability
Monitor for blocklistings that prevent email delivery.
IPv4 & IPv6 Support
Support for IPv4, IPv6 addresses, and netblock monitoring.
Domain Monitoring
Monitor domains against URI blocklists to protect brand reputation.
Instant Alerts
Immediate notification when listings are detected through your preferred channel.
Detailed Reports
Historical reporting and shareable public reports for compliance.
What Does Blacklist Monitoring Check?
150+ data sources: the major RBLs and URIBLs, DNS security filters, ISP reputation systems like Microsoft SNDS, and phishing and malware feeds.
A Blacklist Monitoring
Service vs Doing It Yourself
A cron job, a list of hosts, and a list of DNSBL queries is a working proof of concept. The problems start at scale. Each data source has its own query conventions, rate limits, and failure modes; some need registered access, some change their zones without notice, and some aren't available over public DNS at all.
The alerting is usually harder than the checking. Useful alerts need deduplication, protection against lists that flap, routing to the team that owns each host, and more than one delivery channel. For most production senders, building and maintaining that costs more than a service does.
Blacklist Monitoring Service FAQ
What the service does, what it checks, and how alerts reach you.
What does a blacklist monitoring service do?
It checks your IP addresses and domains against RBLs, URIBLs, DNS security filters, and threat intelligence feeds on a schedule, and alerts you as soon as one lists you, so you can fix the cause before it hurts deliverability.
How is it different from running DNSBL queries myself?
Manual queries work for a few IPs against a few lists. A service checks 150+ sources on a schedule, confirms a listing from several monitoring locations before it alerts, and routes the alert to the right team.
Which data sources are included?
150+ sources: 90+ IPv4, IPv6, and domain blacklists, including Spamhaus, Barracuda, SpamCop, UCEPROTECT, Abusix, and SURBL, plus 24 DNS security filters, URLhaus, and Facebook ThreatExchange. Paid plans add premium sources such as Microsoft SNDS, Google Postmaster Tools, and PhishTank. See the full list.
How are alerts delivered?
By email, SMS, Slack, Microsoft Teams, Google Chat, Discord, Telegram, PagerDuty, Opsgenie, Pushover, Datadog, AWS SNS, CloudWatch, or webhook, routed by host, profile, or alert type.
Is there a free tier?
Yes. The free plan monitors one host every 48 hours against 100+ data sources, with no time limit. Paid plans add hosts, faster checks, and premium sources, with no contracts or minimums.