No More Outages
From Expired Certificates
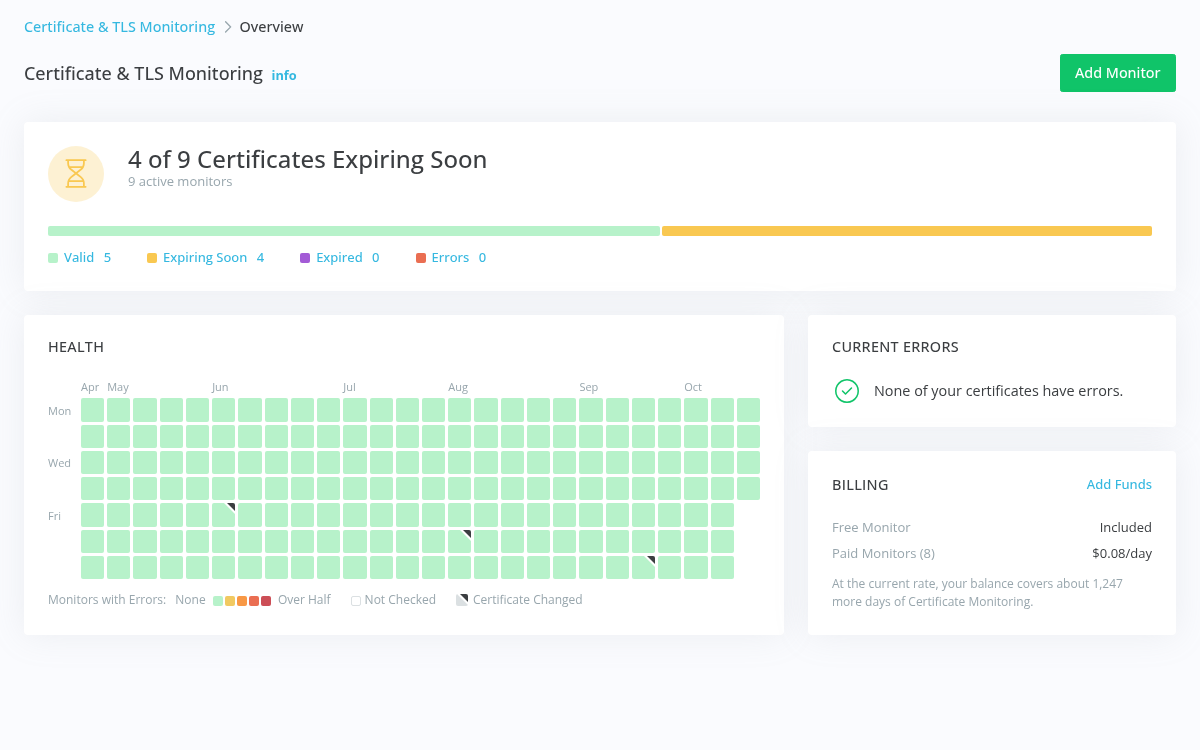
Expired and misconfigured certificates still take down sign-ins, APIs, and checkouts. Watch every certificate on every address, public or private, and hear about it while there's still time to renew.
Renewals Fail
Quietly
Most certificate outages aren't surprises. The renewal was automated, and the automation broke: a DNS challenge that stopped validating, a load balancer that kept serving the old certificate, a node that never picked up the new one.
With certificate lifetimes shrinking toward 47 days, renewals happen more often, and every one is another chance for that to happen.
What Changes
When You Turn It On
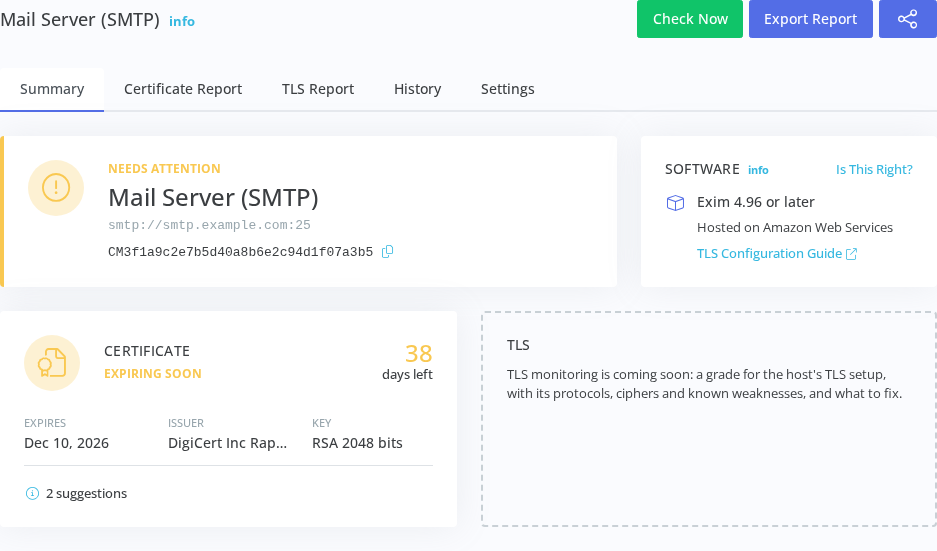
Set thresholds anywhere from 0 to 90 days out, per monitoring profile, so production warns early and staging stays quiet.
Each check reads the certificate from every IP behind the hostname, so a node that missed the renewal shows up right away.
A renewed certificate can still be wrong. Every check validates the chain, the names it covers, and whether it was revoked.
A small agent watches internal services and private CAs without opening your network to the internet.
Set Up Once,
Then Let It Watch
Websites, APIs, mail servers, and anything else on TLS, on any port, including STARTTLS.
Production, staging, and internal services each get their own alert timing and channels.
Get the warning with weeks to spare, and a confirmation when the new certificate is live everywhere.
Further Reading
 White Paper
When Certificates Expire
Anatomy of a preventable outage: seven years of public expiry incidents, the coming 47-day certificate lifetime, and why renewals silently fail.
 Case Study
Automated, and Still Expired
A SaaS platform automated every certificate renewal with Let's Encrypt, then had two certificates expire in fifty days. Automation needs a backstop.
 Datasheet
Certificate Monitoring Datasheet
Continuous certificate validation across your domains, services, and internal infrastructure: expiry, chain, identity, and configuration. Five-page datasheet.
Frequently Asked Questions
Common questions from teams like yours.
We automate renewals with ACME. Do we still need this?
Automation is exactly what this backs up. Monitoring checks that the renewal actually happened and reached every server, instead of trusting that it was scheduled.
Can it watch certificates that aren't on the internet?
Yes. The private network agent runs inside your network and checks internal services and certificates from private CAs.
Is there a free option?
Yes. Your first HTTPS certificate monitor is free, with no trial period and no credit card.
More Solutions
Never Miss a Renewal Again
Your first HTTPS monitor is free. Add it in under a minute.