Evidence Your Auditor
Will Actually Accept
Frameworks ask you to keep encryption in transit working and to know when it breaks. Continuous checks, a dated history of every change, and exportable reports turn that requirement into evidence.
A Screenshot Isn't
a Control
Auditors don't want to hear that certificates are renewed automatically. They want to see that someone would have known if one wasn't, and when it was fixed.
Collecting that by hand every quarter is slow, and it only proves things were fine on the day you looked.
What Changes
When You Turn It On
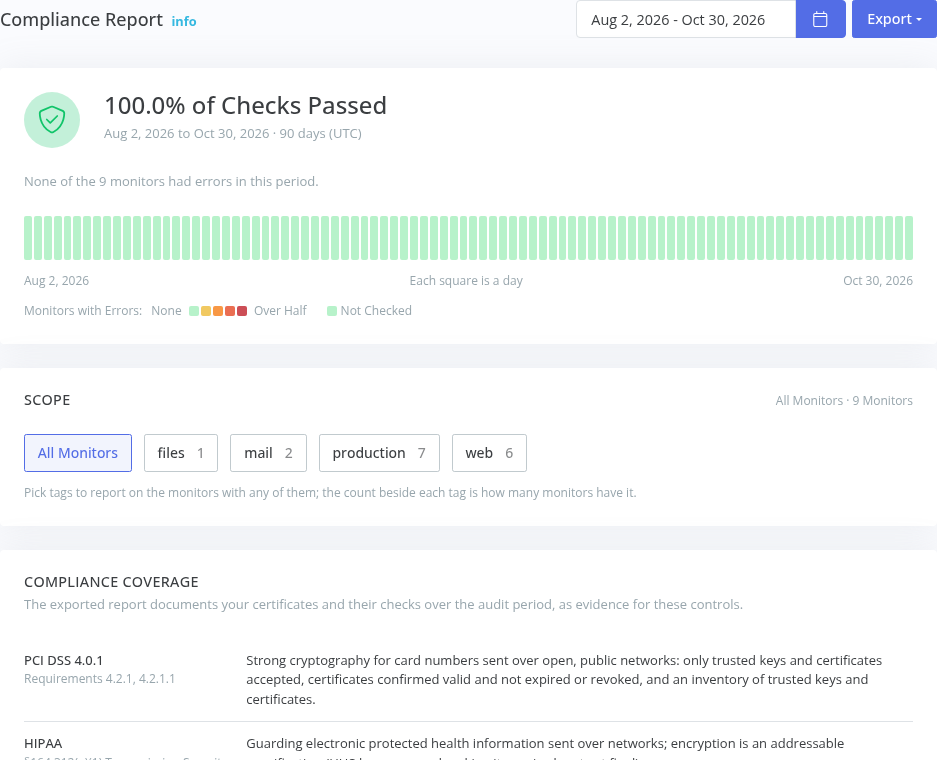
Checks passed over the last 90 days, mapped to the PCI DSS, HIPAA, and NIST SP 800-53 controls they support.
Renewals, replacements, new issuers, and failures are recorded with the date, per monitor.
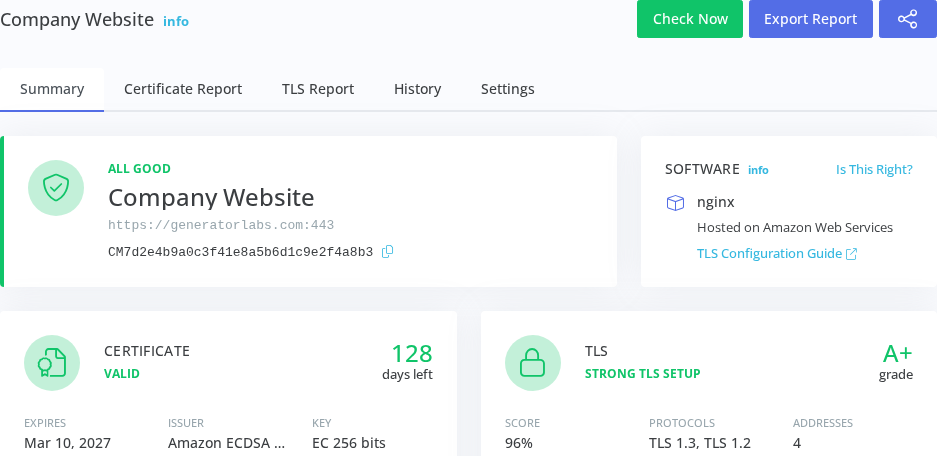
Protocols, ciphers, and known vulnerabilities, graded A+ to F with the fix for each finding. In beta.
Export a monitor's report to PDF, or share a public report link that stays current.
Set Up Once,
Then Let It Watch
Add the endpoints your framework covers: cardholder data, health information, customer-facing services.
Checks run on their own schedule, and every failure and change lands in the history with a date.
Pull the compliance report and per-monitor PDFs instead of a week of screenshots.
Further Reading
 White Paper
When Certificates Expire
Anatomy of a preventable outage: seven years of public expiry incidents, the coming 47-day certificate lifetime, and why renewals silently fail.
 Datasheet
Certificate Monitoring Datasheet
Continuous certificate validation across your domains, services, and internal infrastructure: expiry, chain, identity, and configuration. Five-page datasheet.
Frequently Asked Questions
Common questions from teams like yours.
Which frameworks does the compliance report cover?
It maps certificate checks to PCI DSS 4.0.1, HIPAA, and NIST SP 800-53. The same history supports SOC 2 and ISO 27001 evidence for certificate management.
Does the compliance report include TLS?
It covers the certificate checks. TLS grades and findings are in each monitor's report and its PDF export.
How far back does the history go?
Every monitor keeps its change history from its first check, and the compliance report covers the last 90 days.
More Solutions
Make the Next Audit Easier
Start free, and have 90 days of evidence by the next one.