RSA vs ECDSA: Choosing Certificate Key Algorithms
ECDSA P-256 is the right default for new certificates: smaller keys and faster signing, with RSA as a fallback for legacy clients. Numbers, commands, config.
Read more
Wildcard vs SAN Certificates: Choosing the Right One
A wildcard covers every subdomain from one key; a multi-SAN cert names each host. One hides your hostnames, the other limits the damage. Default to named certs.
Read more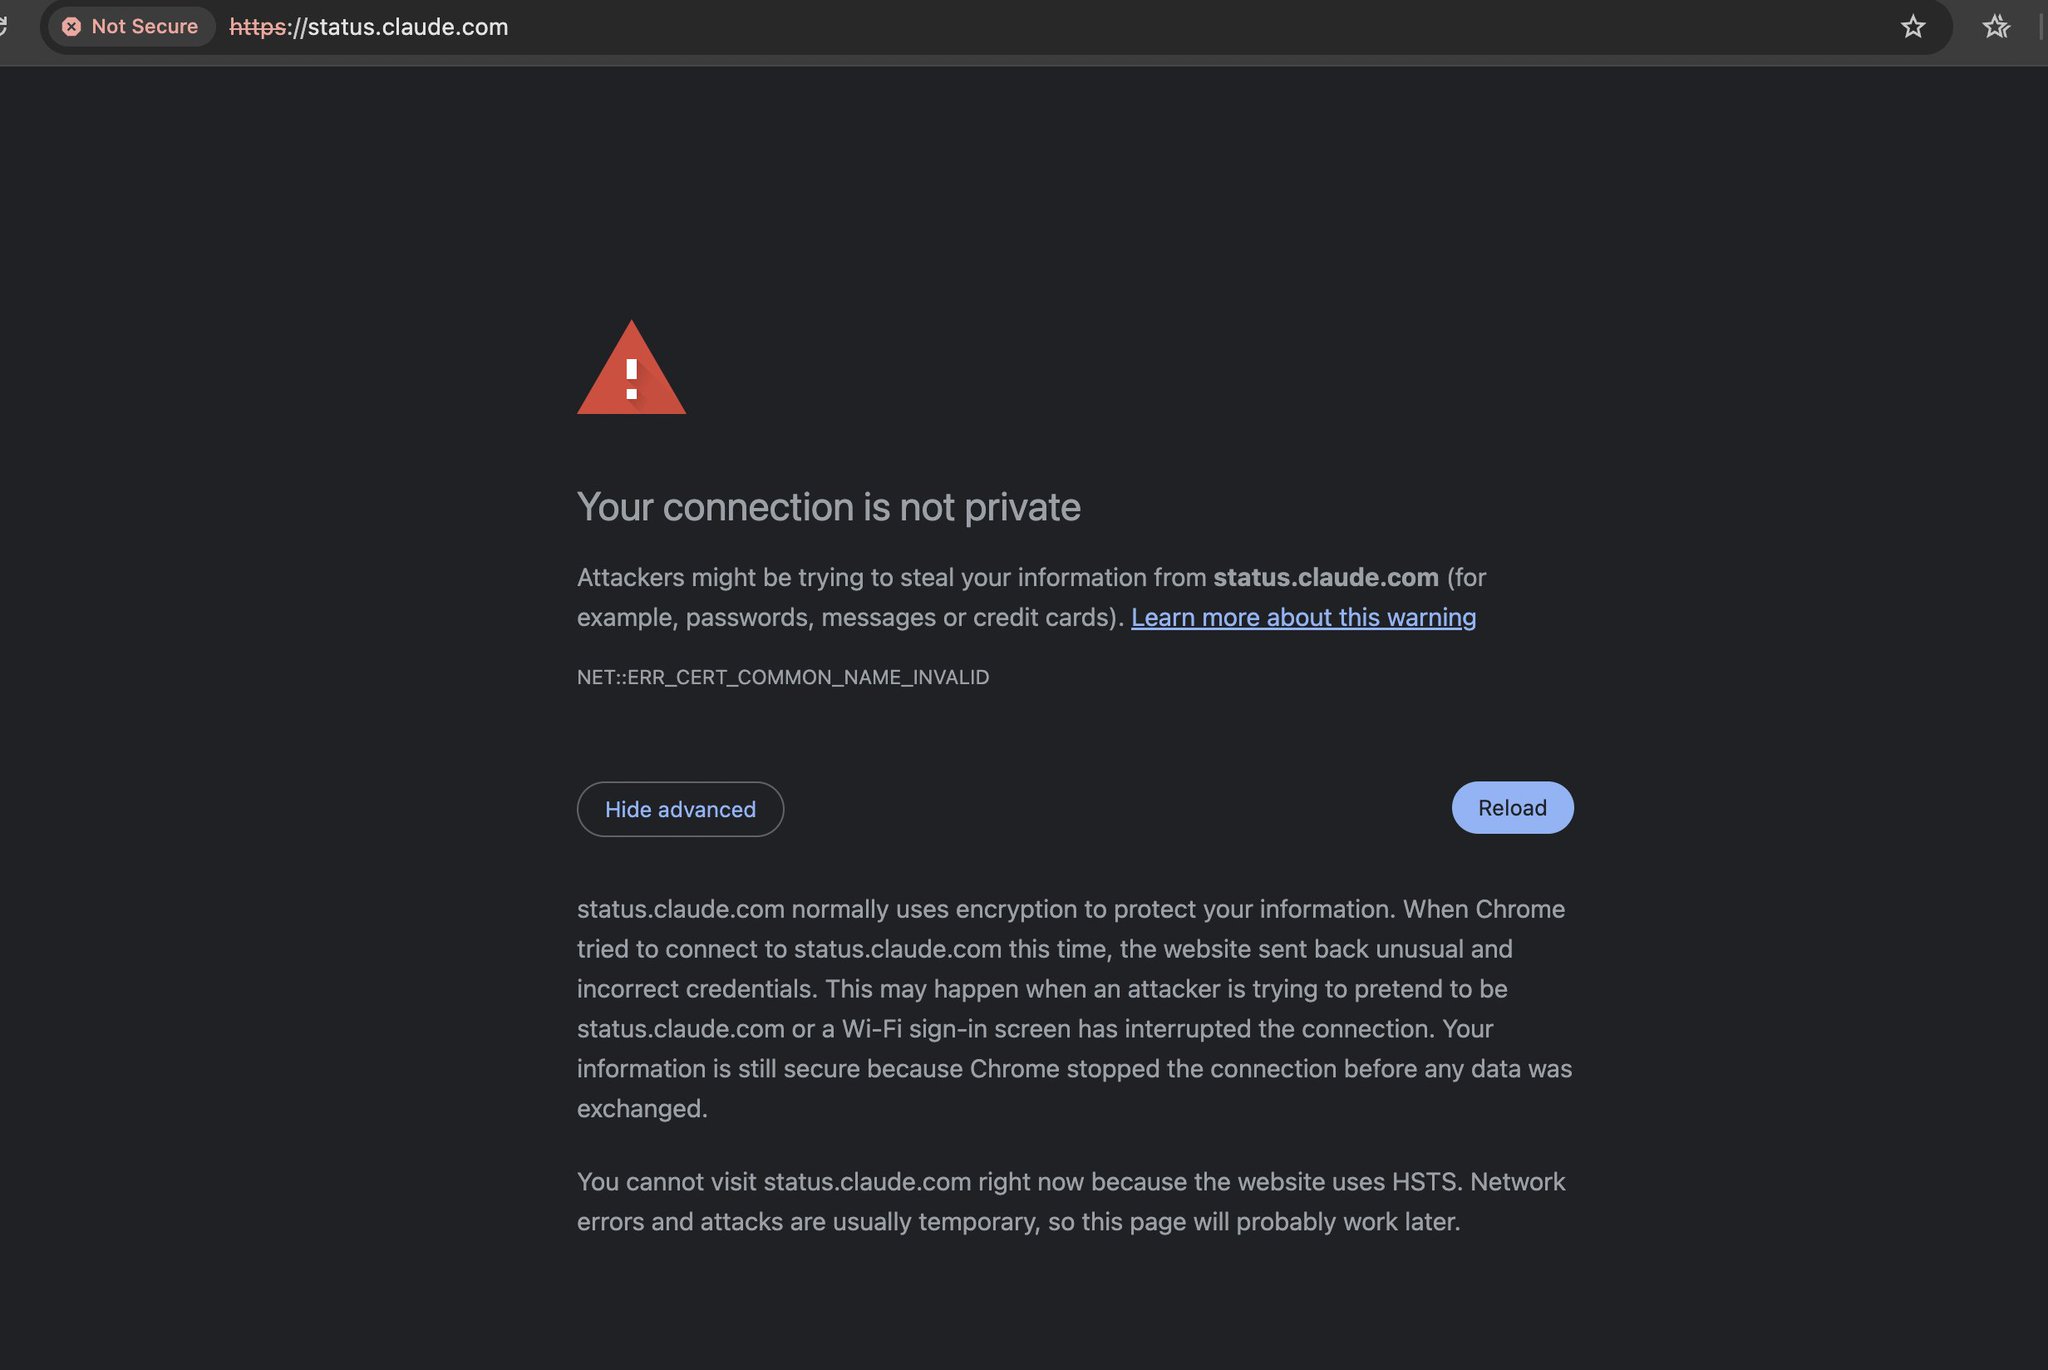
When a Certificate Takes Down the Status Page
On August 14, 2026, an invalid TLS certificate blocked Claude's own status page. If a near-trillion-dollar company can miss a certificate, so can you.
Read more
Shared vs Dedicated Sending IPs: Managing Blacklist Risk
A dedicated sending IP sounds like an upgrade, but for most senders it is a self-inflicted deliverability wound. Here is when each model is the right call.
Read more
Why Certificate Chains Break (and How to Catch It)
A certificate chain that works in your browser can fail for API and mobile clients. Here is why chains break and how to verify one from outside.
Read more
CAA Records: Controlling Who Can Issue Your Certificates
A CAA record names which CAs may issue certificates for your domain. One DNS line closes off a whole class of mis-issuance. Here is how to use it.
Read more